Compliance Without Borders: An Interview with Mark Young
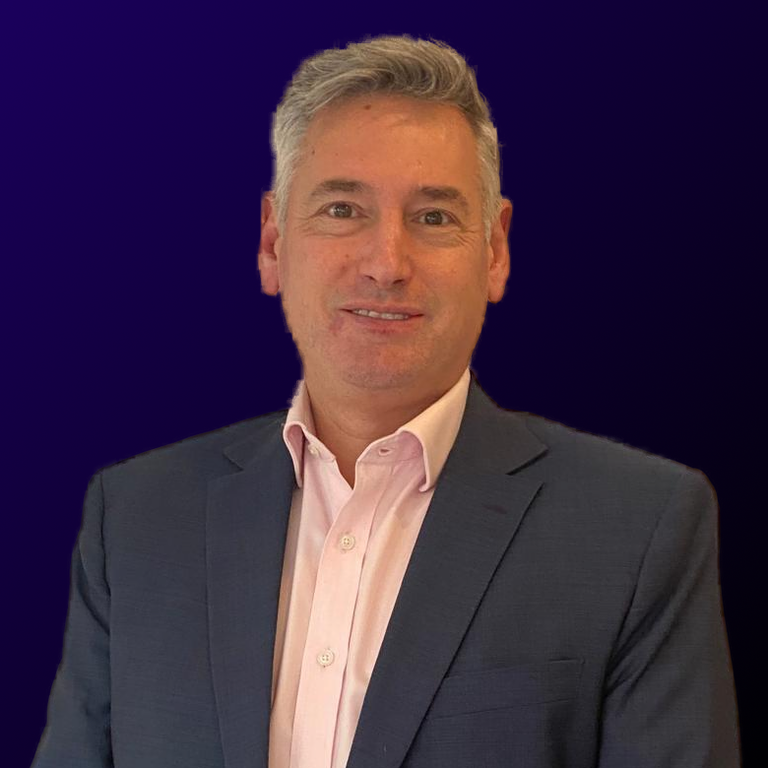
Murray Grainger, Case IQ Senior Compliance Consultant, interviews Mark Young
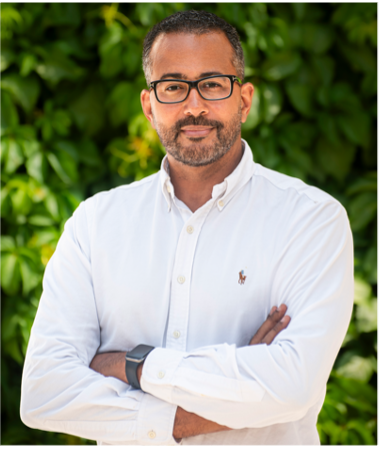
Mark Young is a US-qualified lawyer and ethics and compliance professional with more than 25 years of experience. He began his career at the US Department of Commerce and has spent most of his career in the UK and Europe, with roles at EY and Deloitte, in-house at Google and as Global Head of Ethics & Compliance for a former SoftBank Group company. His experience includes ABAC, investigations, competition, sanctions and export controls, data privacy, whistleblowing programmes, third-party-risk and compliance programme design. Having lived and worked in North America, the UK and the EU, Mark brings a practical perspective on how regulatory requirements and workplace cultures affect the implementation of global compliance programmes.
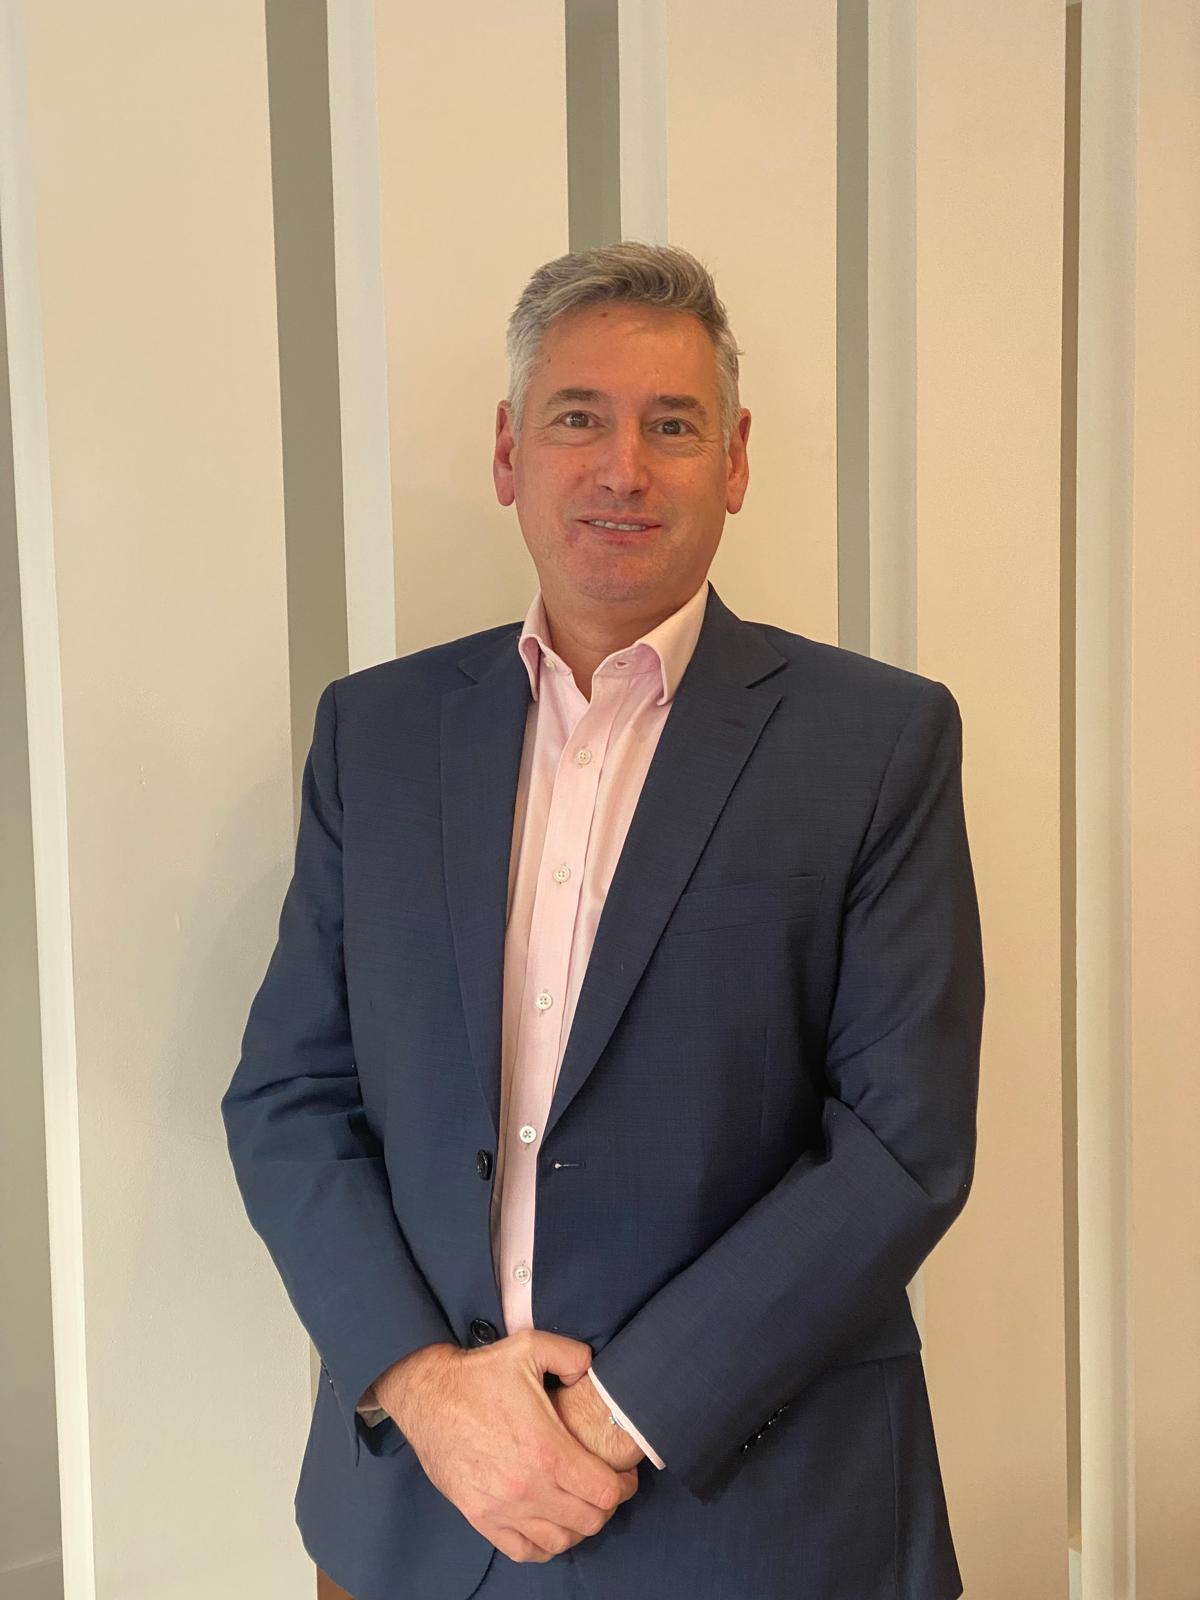
Murray Grainger is has 25 years experience as private practice lawyer, in-house counsel, head of compliance, founder and managing director, business partner, country manager and consultant. His focus is on delivering great customer service, compliance solutions including whistleblowing, TPRM and due diligence and trainings for boards and leadership teams. He currently works as a Senior Compliance Consultant for the UK and EU at Case IQ.
Murray: As a US lawyer who has worked most of your career in the UK and the EU, how do you navigate the different regulatory approaches?
Mark: My starting point is that compliance functions in the US, the UK and EU seek many of the same outcomes: preventing misconduct, establishing accountability and protecting the business and its people. But the legal route and regulatory emphasis can differ.
The practical lesson is not to assume that a process designed at headquarters can simply be exported. Start with the objective, identify the jurisdictions and requirements involved and then determine the appropriate local route to the same compliance outcome.
Murray: Can you share some practical examples?
Mark: ABAC [Anti-Bribery and Anti-Corruption] is a good example. As a US lawyer, the FCPA is naturally an important reference point, but an international compliance programme cannot simply export an FCPA framework. More broadly, the UK Bribery Act and other applicable extraterritorial and national anti-corruption laws need to be considered, along with differing approaches to issues such as gifts and hospitality, interactions with public officials and local enforcement environments. The aim is to establish a strong global standard while ensuring that the programme also reflects applicable local requirements.
Competition and antitrust is another good example. The underlying objectives of protecting competition may be similar, but EU and UK competition law and US and Canadian antitrust law do not necessarily approach every issue in the same way. Distribution arrangements, information exchanges, market power and vertical restrictions may require different analysis depending on the jurisdiction. For ethics and compliance practitioners, this means recognising when a commercial practice or control which works well in one market needs to be reconsidered before being applied elsewhere.
Third party due diligence is another area where I learned not to confuse global consistency with identical treatment. A multinational can have one global risk methodology and minimum standard, while the diligence, approvals and controls applied to a distributor, consultant or intermediary reflect the risks of the particular market and relationship. For example, a third party operating in a high-risk market, interacting with public officials or being paid through an unusual structure may warrant enhanced diligence and additional controls.
The common thread is to separate the compliance objective from the particular process used to achieve it. Global consistency matters, but it does not always require an identical process in every jurisdiction.
Murray: Does “whistleblowing” mean different things across cultures?
Mark: It can, yes. A company can offer the same reporting channel, confidentiality protections and non-retaliation commitment across countries, yet employees may not experience or trust that system in the same way. Attitudes towards hierarchy, challenging a manager, reporting a colleague, anonymity and institutional trust can influence whether and how people raise concerns.
Some of this reflects different legal, institutional and historical experiences. In former communist countries in Central and Eastern Europe, for example, memories of state systems which encouraged informing on colleagues or neighbours can give the idea of “reporting” a very different cultural resonance for some people. More broadly, attitudes towards loyalty to colleagues, confidentiality and challenging authority can vary considerably across cultures. For compliance practitioners, the point is not to generalise about nationalities, but to understand what may influence whether employees in a particular environment are willing to speak up and which reporting channels they are most likely to trust.
It is also important to note that a confidential channel is not automatically a trusted channel. Reporting volumes alone do not tell you whether a reporting culture is healthy. A low number of reports, for example, could mean there are few concerns, but it could also mean employees are reluctant to raise them. I would also look at whether employees know where to report, whether they use managers, HR or employee representatives as reporting channels, whether they understand what happens after a report, whether they fear retaliation, and whether they believe senior employees will be treated consistently.
So the practical question is not simply, “Do we have a whistleblowing channel?” but “Do employees understand it, trust it and believe that using it will lead to a fair response?”
Murray: How important is cultural awareness when assessing compliance risk?
Mark: One of the most useful habits I have developed internationally is to separate three concepts that can easily be conflated: different, higher risk and improper.
A practice may be unfamiliar to someone trained in another market, without being problematic—such as a different approach to relationship building or hospitality. Other circumstances may legitimately increase risk and call for additional due diligence, approvals or controls. And some conduct may cross the line into a policy or legal violation, regardless of whether it is common practice locally.
The practical approach is to understand the context first, identify the actual legal, ethical and reputational risk, and then decide whether the practice is acceptable, needs additional controls or should not proceed. This avoids two opposite mistakes: “We don’t do that where I’m from, so there must be a compliance problem” and “This is how business is done here, so it must be acceptable”. Cultural awareness should improve risk assessment, not replace it.
Murray: How do you reconcile global principles with local implementation?
Mark: This comes down to distinguishing between the core standards or outcomes and how they are put into practice. Certain expectations, like no bribery, no retaliation, fair investigations and appropriate escalation of concerns, should be clear across the entire global organisation. But local law, risk and culture may require different procedures, controls, examples or communications.
For example, a company may require credible allegations to be investigated globally, while the permissible way to access employee communications can differ locally. A global gifts and hospitality standard may be supported by different approval thresholds or examples based on local risk. And a common whistleblowing commitment may need different communications or workflows to reflect local requirements and employee expectations.
The practical test I use is: what outcome or principle is non-negotiable, and what part of the process can legitimately be adapted without weakening it?
Murray: What does this mean in practice for cross-border investigations?
Mark: In my experience, cross-border investigations are where some of these regulatory and cultural differences become very tangible. At the outset, I would map where the relevant employees and data are located and identify applicable privacy, employment and monitoring rules, works council or employee representative rights, privilege considerations and any restrictions on cross-border data transfers.
The investigative objective may be the same in the US, the UK and the EU, but the legal framework for achieving it may differ. For example, accessing an employee’s email in an EU country may require consideration of the GDPR, local privacy and employment law and restrictions on employee monitoring. The US and the UK have their own legal requirements, of course, but the point is that an investigation process developed in one jurisdiction should not automatically be replicated in another.
These differences can also affect the sequencing of an investigation. Before collecting data or conducting interviews, it may be important to understand how local privilege rules affect the investigation and to involve Legal, HR, Privacy, Information Security and/or Internal Audit as appropriate. If a particular method of obtaining information is restricted, I would ask: what are we trying to establish, what information do we legitimately need, and what lawful alternative will get us there? Local requirements should shape how the investigation is conducted without compromising its objective.
Culture matters as well. Employees may differ in how comfortable they are challenging senior colleagues or speaking openly about a manager’s conduct. Investigators therefore need to think not only about the legal framework, but also about how they establish trust, explain confidentiality and conduct interviews. The goal remains consistent fact-finding, but both the legal framework and the way investigators engage with employees may need to adapt across jurisdictions.
Murray: Can a single case management tool work effectively across different jurisdictions?
Mark: Yes, absolutely. A single global case management tool is really valuable because it can provide consistent intake, case categorisation, audit trails, reporting and visibility across the organisation. But “single tool” should not mean “single workflow everywhere.” The configuration needs sufficient flexibility to accommodate local requirements, whether through role-based access, confidentiality controls, language options, retention rules, escalation paths or jurisdiction-appropriate investigation workflows.
The technology should support the way the compliance programme works, rather than force every country into the same process. I would keep things consistent where that makes sense, while allowing flexibility for local law and requirements. The same goes for reporting: global data can show useful trends, but you still need to understand what is happening locally before drawing conclusions.
Murray: Finally, how has working in the UK and Europe changed the way you practice compliance?
Mark: My US legal training remains the key foundation for how I approach compliance: identify the risk, establish the facts, document decisions and ensure accountability. Nearly two decades of working in the UK and Europe has added another perspective—I have learned to ask not only “What does the policy or law require?” but also “What is the objective, what does local law require, how will employees experience this process and can we achieve the same objective in a different way?”
Working across different cultures has also taught me not to assume that people communicate, build trust or respond to authority in the same way. What may seem appropriately direct in one environment can feel overly confrontational in another. An approach intended to build relationships in one culture may be viewed as unnecessarily indirect in another. For compliance officers and investigators, understanding those tendencies can make a real difference in how we communicate expectations, conduct training, ask questions and build trust.
One of the greatest values of practising internationally is learning to act as a “translator.” Not just between laws, but between global expectations and local realities. For me, it is not about judging that one system is better than another. It is about preserving the principles that matter, understanding the regulatory and cultural environment in which they operate and finding a practical way to make compliance work.
How Case IQ Can Help Multi-National Compliance Teams
Case IQ offers a suite of tools to ensure compliance and investigation teams can manage risk from end to end. Our solutions include:
- Whistleblower hotline
- Investigative case management software
- Compliance monitoring
- Quantum Approvals & Disclosures
- Third-party management
By implementing one or more of these solutions, teams can manage risk, keep sensitive data secure, resolve issues faster, and prevent incidents, all from one trusted provider. Whether you are a small business or a global enterprise operating across multiple countries, Case IQ can be scaled and configured to your needs and workflows.
Book a demo today to learn how Case IQ's suite of compliance and risk management solutions can help your team.
See Case IQ in Action
Book a personalized demo with one of our experts to see how Case IQ can fit into your processes.
Ready to Transform Your Investigation Process?
Join 80,000+ professionals who trust Case IQ to streamline their case management and ensure compliance.